







Initial Certification - Stage 1
Auditor reviews ISMS documentation to ensure the right policies and procedures are in place.
ISO 27001
Achieve and maintain ISO 27001 certification so you can focus on growing your business globally.
Schedule a demo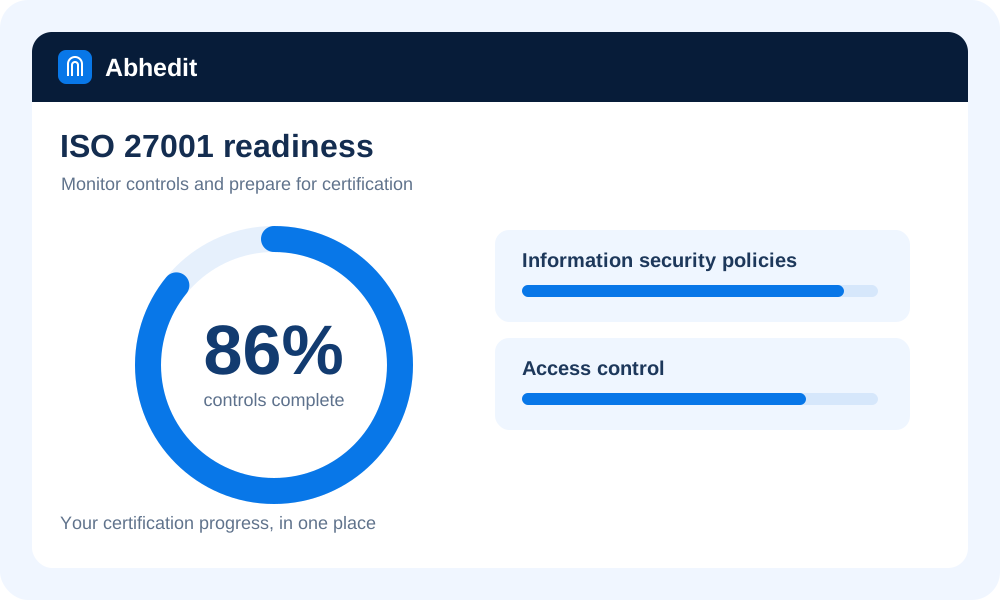
ISO 27001 is a universal standard built for organizations around the globe. ISO 27001 pushes organizations to establish, maintain, and continually improve their information security management system (ISMS) to boost customer confidence.
Auditor reviews ISMS documentation to ensure the right policies and procedures are in place.
Auditor reviews business processes and security controls to prove your ISMS meets ISO 27001 requirements. Passing Stage 2 results in an ISO 27001 certification, which is valid for 3 years.
Evaluate your ISMS and a sample of your controls. Two surveillance audits; one each subsequent year following initial certification.
The recertification audit occurs during the year of ISO 27001 certificate expiration. Similar to Stage 2, this audit evaluates the evidence to prove your ISMS and controls are effective, and that they meet the ISO 27001 requirements. Passing a recertification audit will renew the ISO 27001 certification period for the next 3 years.
ISO 27001 has hundreds of requirements to comply with. Save hundreds of hours achieving compliance while enabling best-in-class security practices.
Create your policies, train your employees, secure your cloud, and manage risks all in one platform.
Make sure you get your ISO 27001 certificate with guidance from our team of experts.
Ensure you have the right controls in place to maintain compliance.
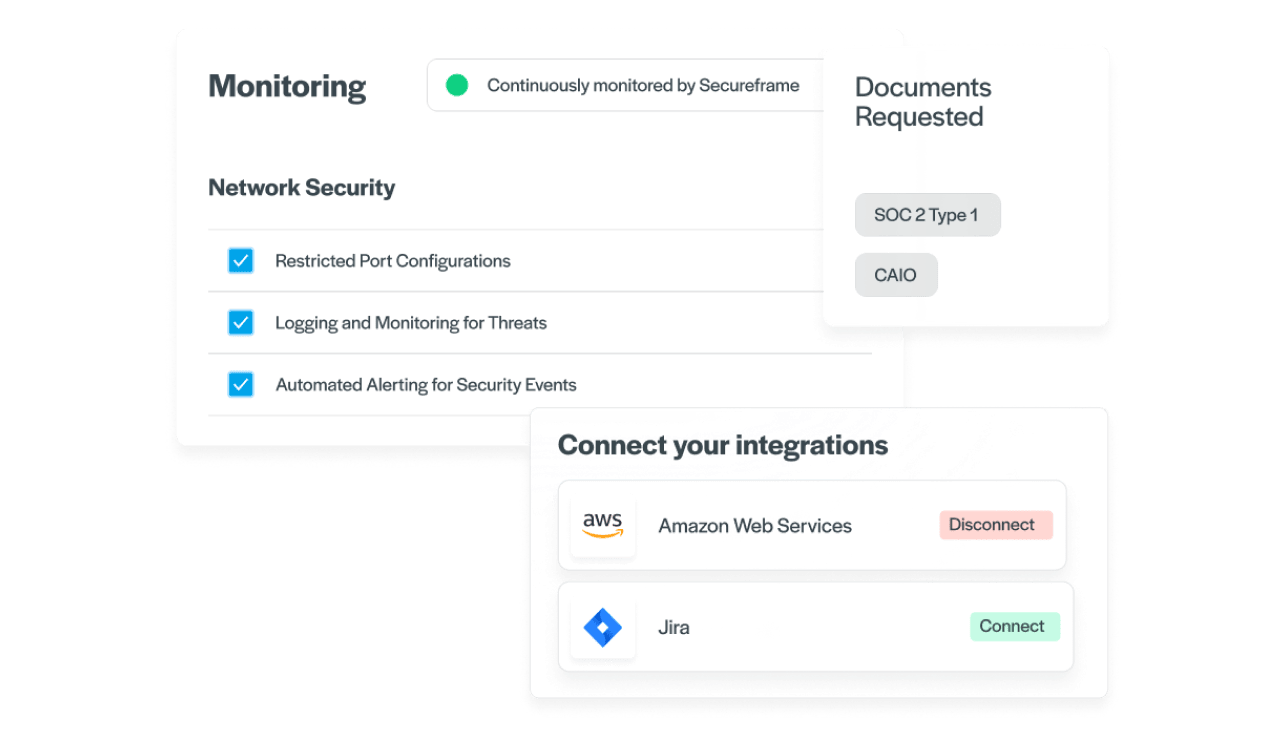
Design an information security management system (ISMS) that aligns with both the ISO 27001 framework and your organization’s goals. Select from our library of policy templates, adapt them for your organization and publish to your employees—all through the Abhedit platform.
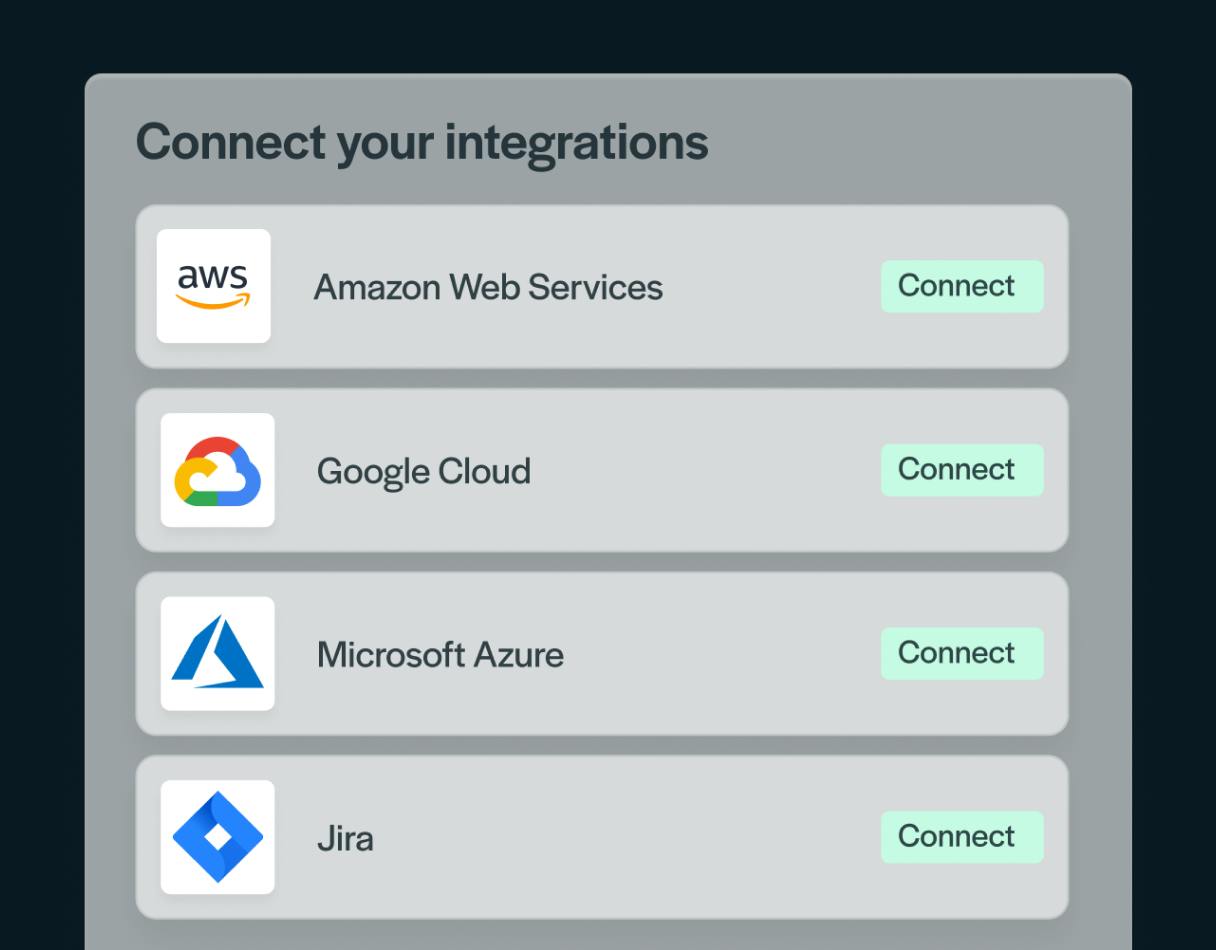
Connect and monitor your cloud infrastructure for ISO 27001 compliance. Plus, no need to install agents — we scan through read-only access.
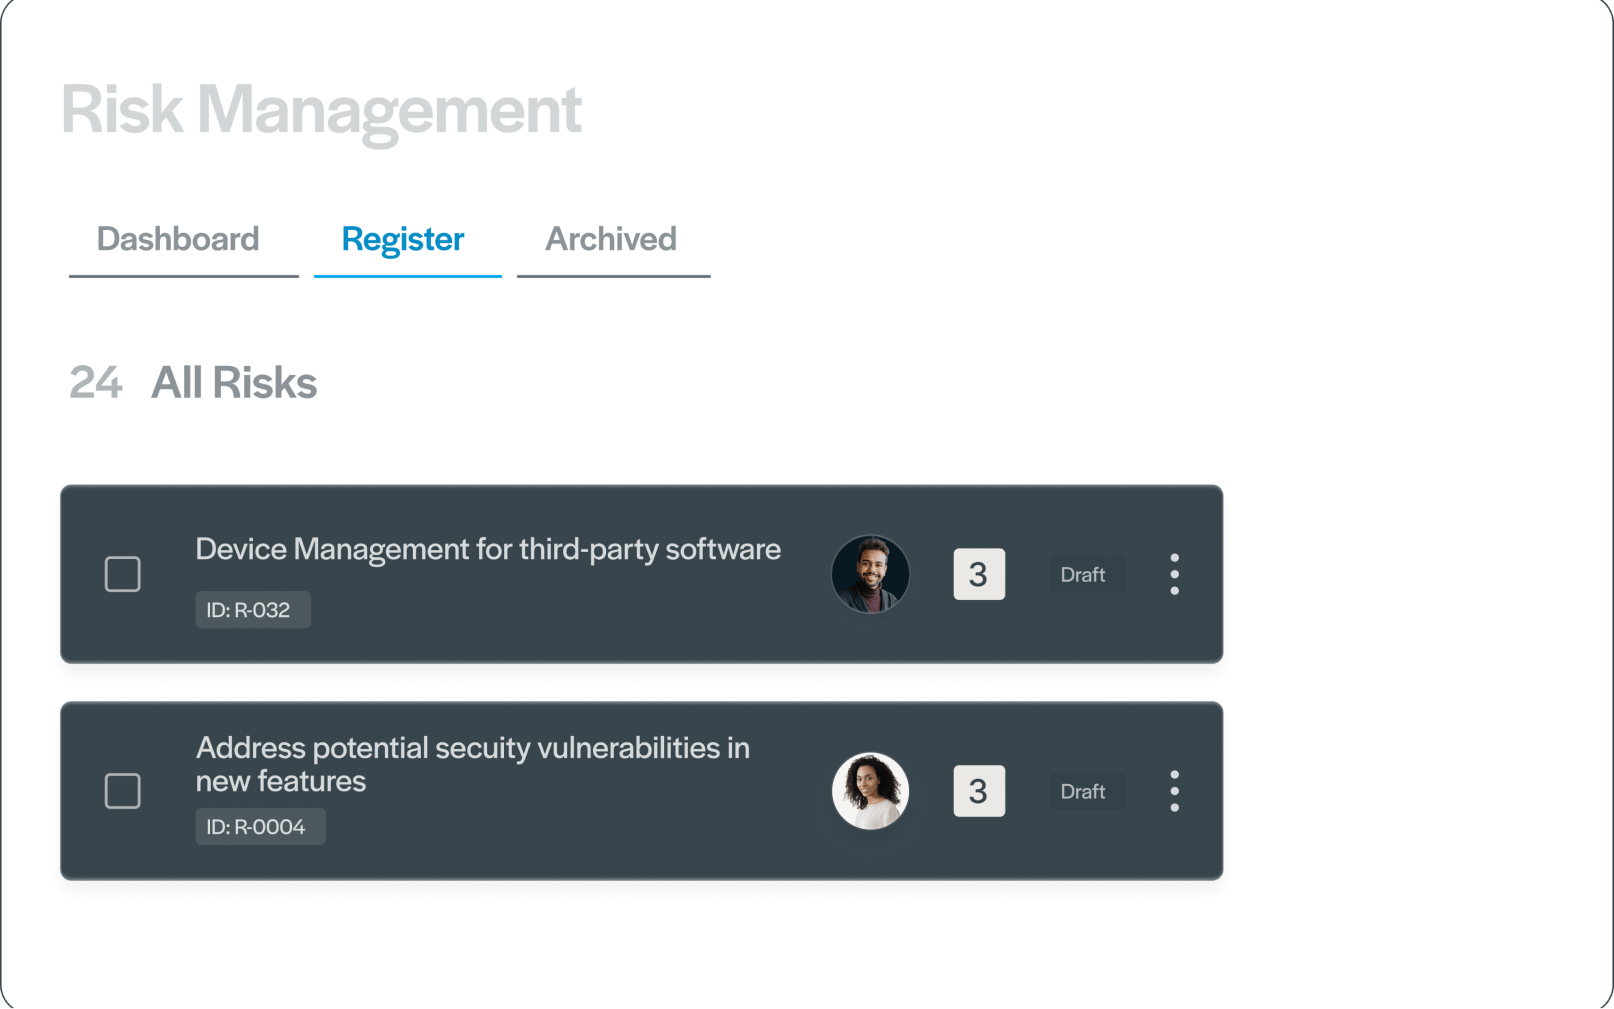
We make it simple for you to complete vendor risk assessments, regularly review vendors and complete required due diligence.
Our workflows streamline the onboarding and offboarding process for your employees. Easily track that your designated in-scope personnel have completed background checks, security awareness training and acceptance of security policies — all through our employee dashboard.
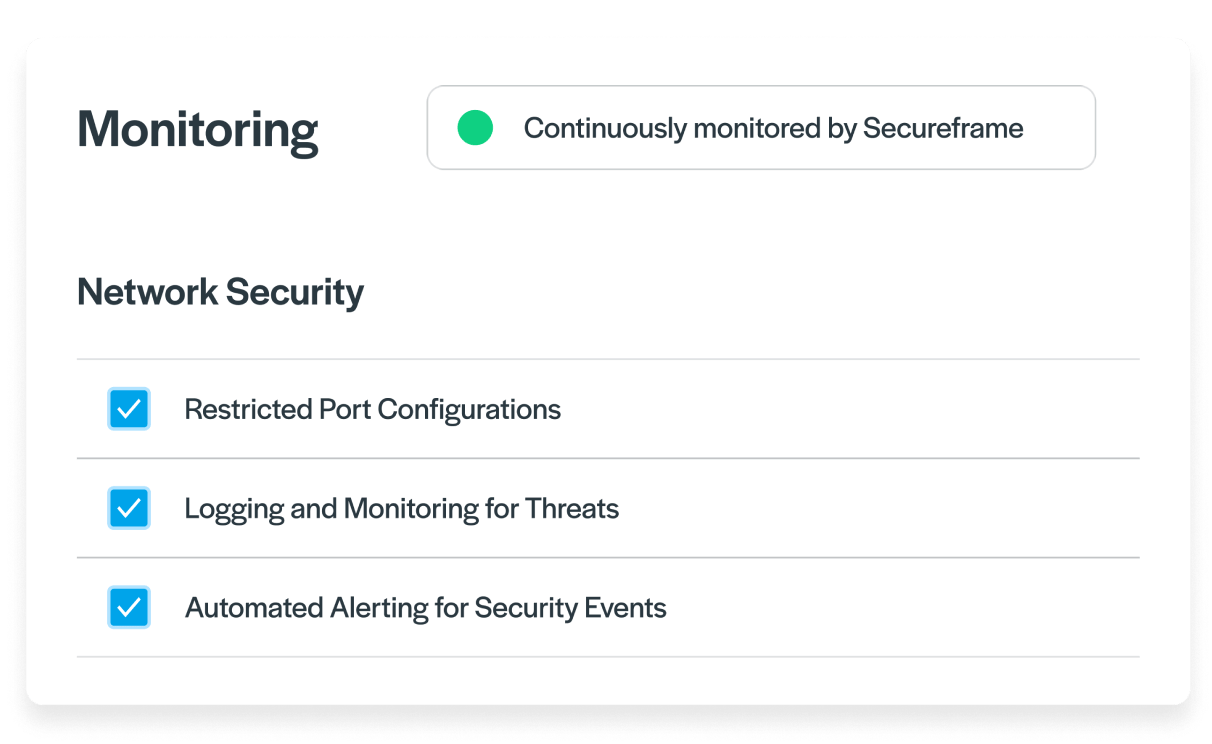
Maintain ISO 27001 certification by continuously monitoring your compliance environment and notifying personnel when regular tasks are due. Ensure security, privacy, and compliance requirements are being met with real-time alerts on nonconformities across your tech stack — so that you can fix them quickly.
Bring security controls, evidence, and risk management together as you prepare for ISO 27001 certification.
Abhedit’s automated compliance platform has a common control layer that makes it easy to apply the same controls you have completed to additional frameworks, so you can save time meeting new standards.
Learn the fundamentals of the ISO 27001 standard and get a step-by-step breakdown of the audit process to help you achieve ISO 27001 certification.
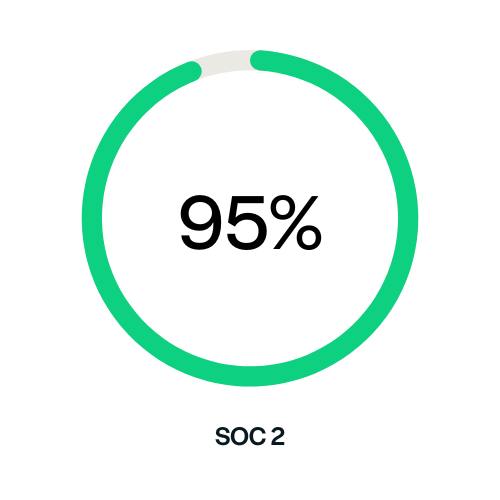
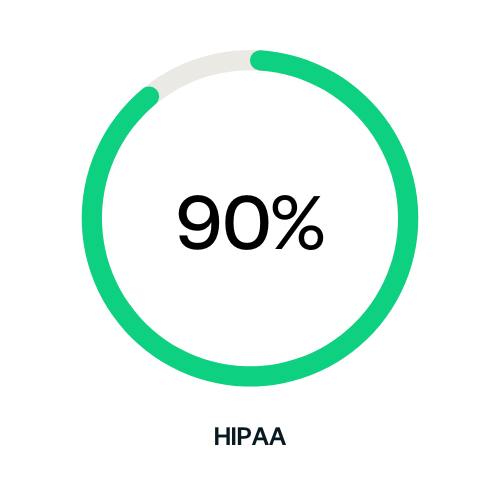
Explore practical guidance for preparing your security program and certification audit.
Explore the checklistAutomated tests, continuous monitoring, and risk management with the support you need — all in one place.
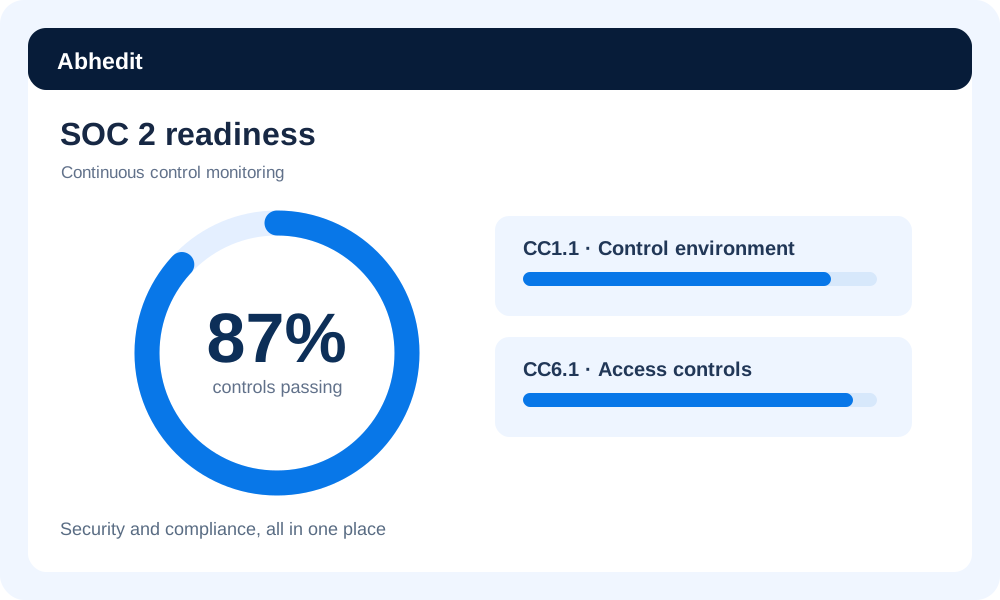
Quickly achieve ISO 27001 certification and strengthen your security posture with automated evidence collection and real-time monitoring.
Demonstrate your security posture and save time responding to security questionnaires to build customer confidence and accelerate sales.